RI Data requirements
Rhode Island's law took effect January 1, 2026 at a 35,000-consumer threshold and contains a disclosure requirement found nowhere else: the privacy notice must identify all third parties to whom the controller has sold or may sell personal data. For a website running dozens of advertising and analytics tags, that is a vendor inventory requirement in disguise, and it has to be accurate. Consumers may opt out of targeted advertising, sale, and profiling, and sensitive data requires opt-in consent. The Attorney General enforces as a deceptive trade practice, with no cure period, penalties of up to $10,000 per violation, and a separate fine of $100 to $500 for each intentional disclosure of personal data in violation of the chapter. Rhode Island is the clearest example of a state law that cannot be satisfied with policy text alone, because the text must list the vendors that are actually receiving data.
RI Data articles and analysis
IAB Multi-State Privacy Agreement (MSPA) Update 2026: What Advertisers Need to Know
A report out of Carnegie Mellon’s School of Public Policy found that “87% (216 million of 248 million) of the population in the United States...
Read More
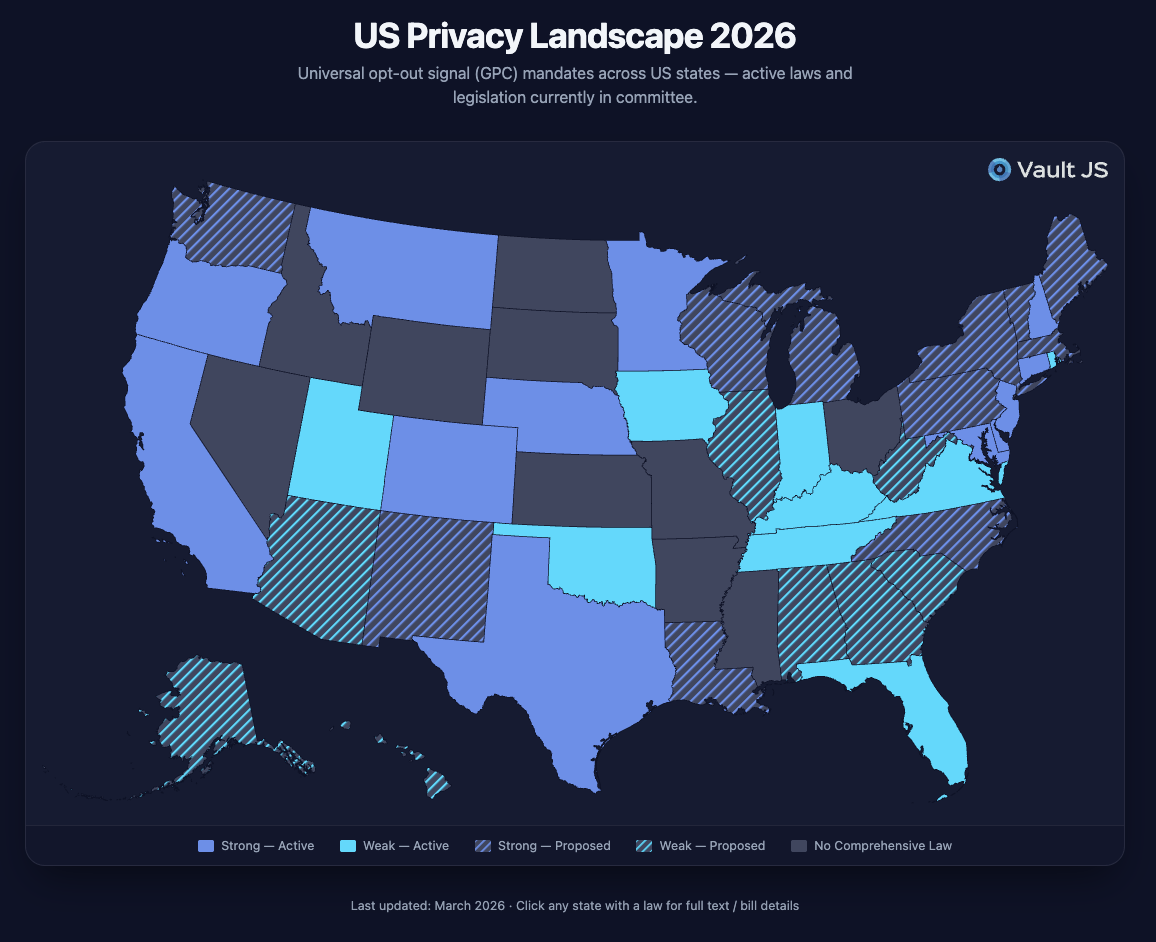
U.S. Privacy Laws (and Key Provisions) That Take Effect or Become Enforceable in 2026
2026 is a turning point in U.S. privacy regulation: multiple new comprehensive state laws go live, enforcement provisions activate, and novel mechanisms (like the California...
Read More
Other US State Privacy Laws
See what your sites and apps actually send
Get a free site analysis: every tracker, mapped to the laws that apply to it.